Manage Integrations
Settings › Integrations is where you connect Plexicus to the external services it works with: source control, issue tracking, secrets backends and APIs, team messaging, on-call alerting and compliance. Which security tools scan your code is configured elsewhere — see Where scanning is configured.
Prerequisites
- A Plexicus account in your organization
- The credentials the service asks for (an OAuth sign-in, a token, a webhook URL, or an instance URL plus credentials — each provider's guide lists exactly what it needs)
- For the Secrets & APIs, Communication and On-call cards: the admin role. Other members can open these cards, but the form is read-only
1. Open Settings › Integrations
- In the left sidebar, click Settings, then Integrations (under Configuration)
- The categories are listed on the left, each with the number of integrations it holds. Select a category to see its cards; the selected category is kept in the page address, so you can bookmark or share it
- Use Search to filter the cards by name or category
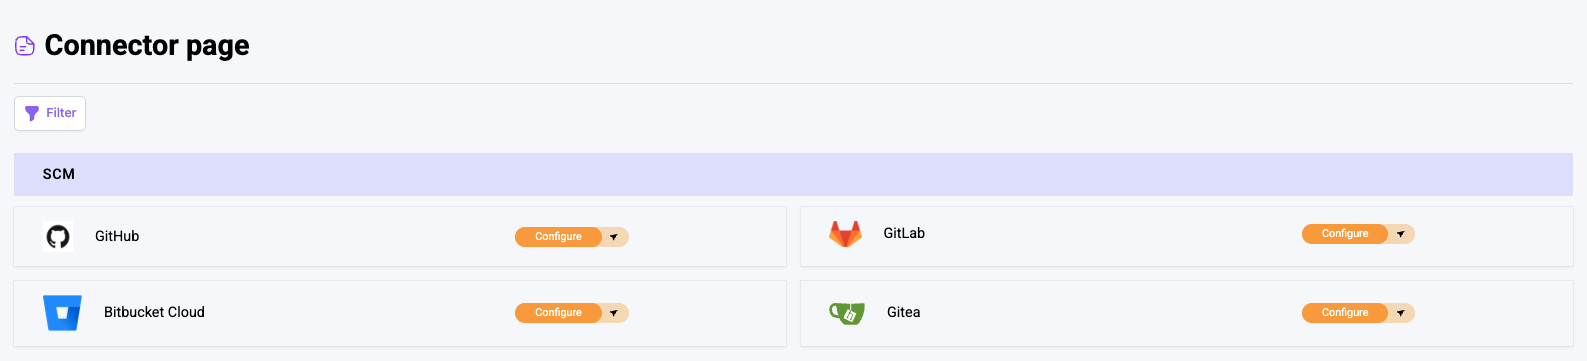
Each card shows the integration's name, FREE or COMMERCIAL, a Description, its status (Enabled or Disabled) and a Configure button.
2. Pick the integration
| Category | Cards | What it is for | Guide |
|---|---|---|---|
| SCM | GitHub, GitLab, Bitbucket Cloud, Gitea, Forgejo, Azure DevOps, Azure TFS | Repositories to scan, and pull requests for fixes | SCM providers |
| Issue tracking | Jira, ServiceNow, Outgoing webhook | Tickets and incidents for findings; a webhook to your own URL when a remediation issue is created | Ticketing Integrations (Jira, ServiceNow); Outgoing webhook |
| Secrets & APIs | HashiCorp Vault, Kubernetes Secrets, OpenAPI, AWS Secrets Manager, GCP Secret Manager, Azure Key Vault | Secrets backends that automations read (and, for the cloud secret managers, write) secrets in, and OpenAPI 3 specifications whose operations automations can call | Connect an integration |
| Communication | Slack, Microsoft Teams | Messages to a channel or incoming webhook | Connect an integration |
| On-call | PagerDuty, Opsgenie | Incidents on a PagerDuty service, alerts in Opsgenie | Connect an integration |
| Compliance | Vanta | Commercial connector; whether you can configure it depends on your plan | Plans & Entitlements |
3. Connect an integration
- Select the category and click Configure on the card
- Fill in the form:
- SCM cards: follow the provider's guide — GitHub, GitLab, Bitbucket Cloud, Gitea, Forgejo or Azure DevOps and Azure TFS
- Jira and ServiceNow: follow Ticketing Integrations
- Outgoing webhook: see Outgoing webhook
- Secrets & APIs, Communication and On-call cards (except OpenAPI): enter a
Name for the connection and the fields the service asks for; keys and secrets such
as an API key are entered directly in those fields. Credentials reference is
optional: an opaque reference to credentials you already store (for example
secret://...), never the secret itself - OpenAPI: enter a Name and the OpenAPI specification URL, then click Fetch operations. Plexicus lists the operations it found; you can save only once at least one operation is listed
- Click Save and test. Slack and Microsoft Teams send a real test message, PagerDuty a real test event and Opsgenie a real test alert, so check the destination you entered
Verify
- After Save and test, the form shows Connection OK when the test passed
- The card's status reads Enabled once the connection is saved — also when the test failed, so check the test result, not only the status
Change or remove a connection
- Click Configure on an Enabled card
- On Secrets & APIs, Communication and On-call cards, edit the fields and click Save, or click Delete to remove the connection. All of them except OpenAPI also have Test connection to re-run the test
- On SCM and issue-tracking cards, use Update (where the form offers it) to change the connection, or Delete to remove it
Outgoing webhook
The Outgoing webhook card (category Issue tracking) sends a webhook to a URL you choose after a remediation issue is created.
- Click Configure on the Outgoing webhook card, then Connect
- Enter a Webhook Name and the Webhook URL, choose the HTTP Method and Data Format, and click Next
- Optional: choose an Authentication Type (Username and Password, or a Bearer Token) and add headers (Header Name, Header Value); click Next after each step
- Check the preview and click Save Webhook. The card then reads Enabled; use Update to change it or Delete to remove it
SCM providers
| Provider | Type | Setup | Pull Requests | Notes |
|---|---|---|---|---|
| GitHub | Cloud | GitHub App (OAuth redirect + installation) | ✓ | GitHub App preferred over a plain OAuth App — it adds webhooks and per-repository install |
| GitHub Enterprise Server | Self-hosted | Instance URL + PAT, or OAuth App, or GitHub App | ✓ | One credential set per connection; the mode is auto-detected |
| GitLab | Cloud | OAuth redirect | ✓ | Uses the deployment-level GitLab application |
| GitLab | Self-hosted | Instance URL + client id + client secret, then OAuth redirect | ✓ | You register the application on your own instance — see Self-Hosted |
| Bitbucket Cloud | Cloud | OAuth redirect | ✓ | Bitbucket Cloud only; Bitbucket Server / Data Center not supported |
| Gitea | Cloud / Self-hosted | Instance URL + personal access token | ✓ | Token only. Grant Organization → Read (read:organization) as well as repository and user read |
| Forgejo | Cloud / Self-hosted | Instance URL + personal access token | ✓ | Token only — same scopes as Gitea, including Organization → Read (read:organization) |
| Azure DevOps | Cloud / On-prem | Personal Access Token (PAT) + organization URL | ✓ | Grant Project and Team (Read), Code (Read & Write), and Work Items (Read & Write). Cloud and Azure DevOps Server / TFS |
| Azure TFS (TFVC) | On-prem | Shared Azure DevOps PAT | ✗ | Team Foundation Version Control, read through your Azure DevOps connection; no PR support |
Self-hosting Plexicus? Callback URLs, scopes and the chart values behind each of these are in the SCM Connection Reference.
Where scanning is configured
Security tools are not cards under Settings › Integrations. They are configured in three places:
- For the whole organization — Settings › Platform › Scan modules. In the left sidebar, click Settings, then Platform. Scan modules turns each Plexicus scan module on or off for the whole organization; click Configure on a module to set its severity filter and advanced options. The modules are described in Security Scanner Bundles
- For one repository — Repo Scan. On the Repo Scan page, click the gear icon (Configure) on a repository's row. The Connectors dialog lists the tools for that repository: use the Enable switch on a tool and click Configure to adjust its settings. Clicking Save Configuration re-scans the repository: Plexicus asks you to confirm, because the re-scan deletes and re-creates the repository and clears its existing findings. A module that is off for the organization can still be enabled here for a single repository. See Configuring Scans
- Results from another tool — Findings › Upload Scan. Open Findings and click
Upload Scan. Choose the repository under Select repository, the tool under
Select tool (
fortify,checkmarx,kiuwan,blackduck,burpsuite,sonarqube,appscanorsarif), the report under Select file, and click Upload. The report's issues become findings on that repository. For Black Duck, see Black Duck
Troubleshooting
Clicking Configure on Vanta opens an upgrade dialog instead of the form
- The Vanta connector is not included in your current plan. Request access from the dialog, or see Plans & Entitlements
"You have read-only access to automations. Ask an admin for edit access."
- Only admins can change Secrets & APIs, Communication and On-call connections. Ask an admin of your organization to make the change or to give you the admin role
"Connection failed" after Save and test
- Read the detail shown under the message, then check the destination (channel, webhook URL, service or address) and the credentials, and click Test connection again
An SCM card still shows Disabled after connecting
- Reload the page. If it still reads Disabled, open the card and repeat the steps in the provider's guide
No card for Black Duck, Checkmarx, Fortify or SonarQube
- These are not integrations cards. Import their reports with Findings › Upload Scan — see Where scanning is configured
Next Steps
Once your integrations are connected, you can:
- Add repositories to scan from a connected SCM provider
- Configure scans for each repository
- Set up ticketing to create tickets from findings